

Main world manufacturers together with Ledger, Salesforce and BBC served cryptocurrency and credit score card-stealing malware to web site guests on Monday, based on safety researchers, the newest in a wave of wide-reaching cyberattacks.
Dubbed “Optimjack” by researcher Amirul Iman, the marketing campaign delivered malicious code by means of web site scripts, together with these hosted by Optimizely, an internet site optimization platform. The malware can exchange respectable cryptocurrency pockets addresses with attacker-controlled alternate options when guests copy addresses. It additionally captured bank card particulars entered into web site types, based on a separate evaluation by cybersecurity agency StepSecurity.
The marketing campaign affected web site scripts belonging to 178 organizations, together with {hardware} pockets Ledger, OANDA / Coinpass and buying and selling platforms IG, Interactive Investor and TMS Brokers, based on Report URI’s investigation.
Different affected manufacturers included IKEA, Salesforce, Zoom, the BBC and CNN — web sites that collectively appeal to tens of millions of holiday makers a day.
A spokesperson for Optimizely confirmed to Cointelegraph on Monday that an unauthorized get together exploited a vulnerability in its Experimentation account signup circulate so as to add malicious JavaScript to some buyer initiatives.
“We now have blocked entry to the weak path and deployed a repair,” they stated. “We now have eliminated the injected code from affected initiatives. We now have additionally ended energetic classes, revoked tokens, and reset entry for affected person accounts. Lastly, now we have blocked any code from being delivered in Cloudflare,” they stated, including that they’re persevering with to analyze and have notified all affected clients.
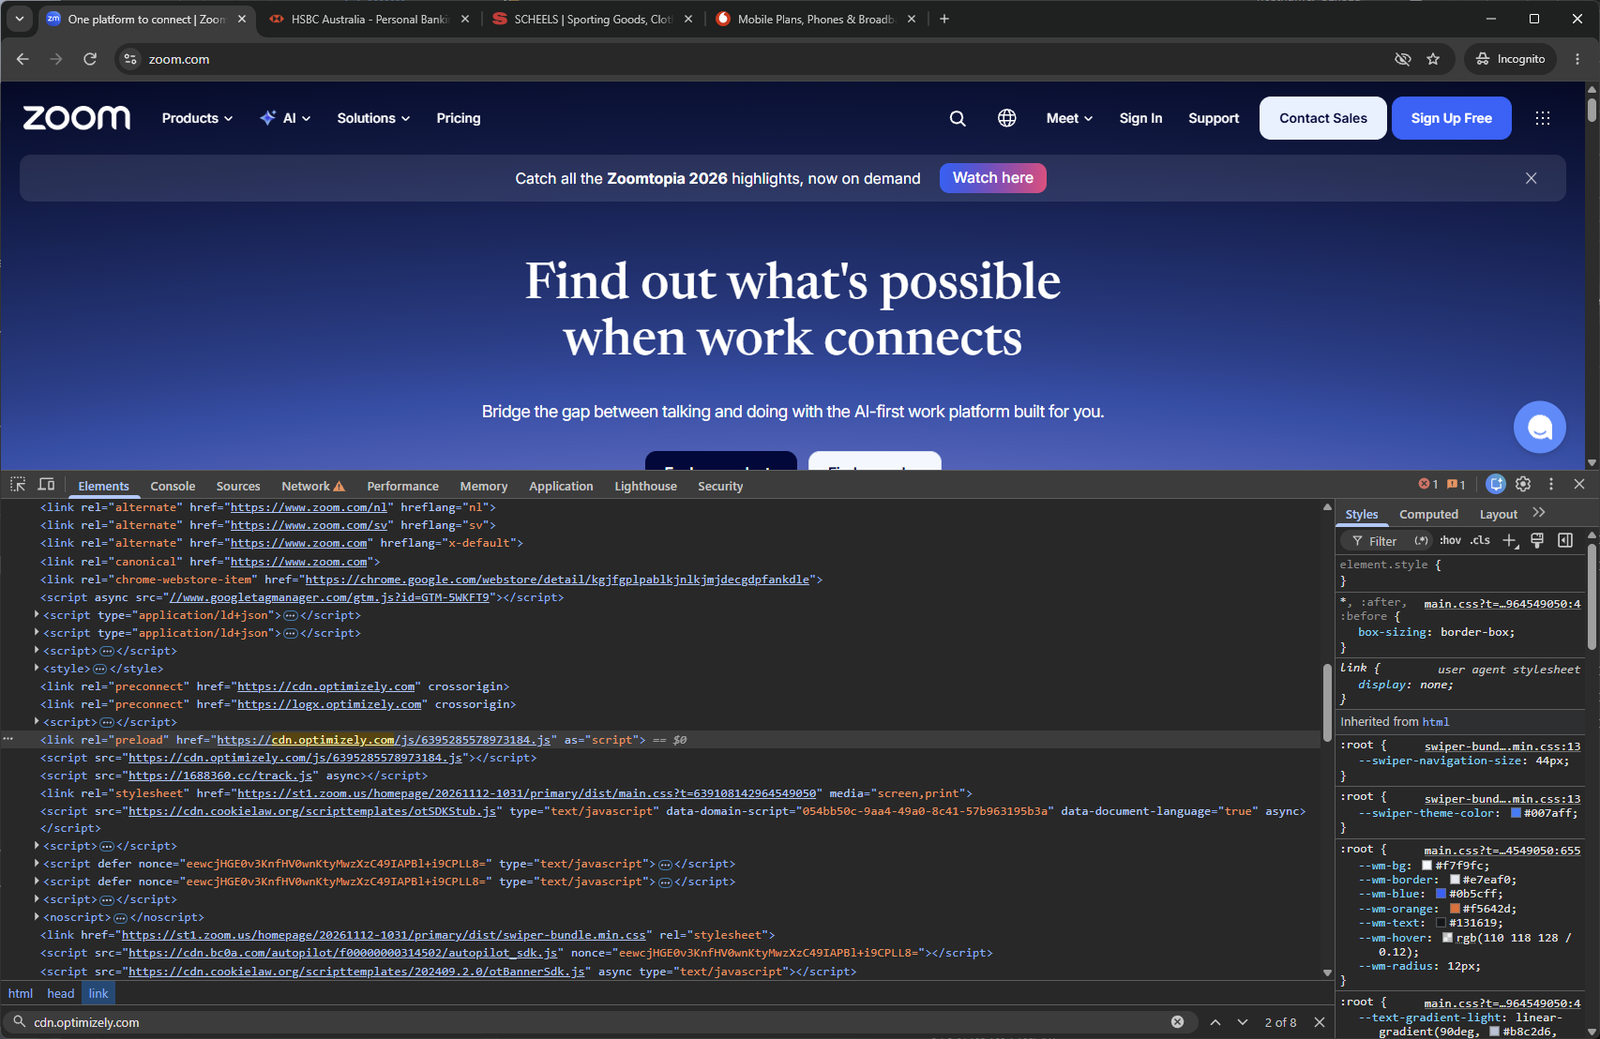
BBC was among the many first web sites seen serving the Optimizely injection at 4:21 am UTC on Monday, based on Report URI CEO Scott Helme. By 9:52 pm UTC, a lot of the malicious code had been eliminated, with Ledger’s snippet cleaned at about 8:41 pm UTC.
Cointelegraph reached out to Ledger, Coinpass, and quite a lot of different main companies reported as impacted by the malicious injection.
How trusted web sites served a theft instrument
Optimizely lets companies run experiments and customized code on their web sites by means of JavaScript snippets. Attackers inserted malicious code into these buyer initiatives, inflicting in any other case respectable scripts to load the malware when guests opened affected pages.
As soon as loaded, the malware might exchange respectable cryptocurrency pockets addresses with attacker-controlled alternate options, together with addresses copied to a customer’s clipboard. A person might then unknowingly paste the attacker’s deal with when making a switch.
Associated: PHP flaw attracts tens of millions of exploit makes an attempt, Cloudflare CEO warns
The script additionally watched for bank card numbers, expiry dates and safety codes entered into web site types and despatched captured particulars to an attacker-controlled server. Nonetheless, it couldn’t learn cost fields remoted inside third-party cost suppliers’ cross-origin frames, StepSecurity stated.
Guests utilizing iPhones and iPads additionally confronted an extra risk: the malicious script loaded code linked to the Coruna and DarkSword iOS exploit kits, based on Helme.
Researchers have but to determine how attackers obtained entry to change the Optimizely initiatives.
Crypto losses stay unconfirmed
Addresses recognized by researchers as linked to the malware obtained roughly $7,100 in cryptocurrency on Monday, based on blockchain information checked by Cointelegraph.
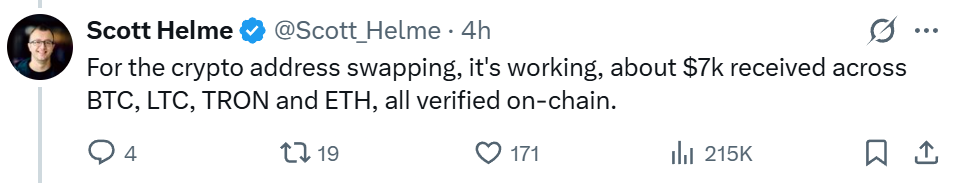
StepSecurity’s separate evaluation put funds obtained or held throughout the wallets at roughly $6,600, whereas noting that some addresses had exercise predating the assault.
Helme stated it couldn’t decide what number of cost card particulars or cookies had reached the attackers’ server.
The marketing campaign follows a string of current threats to web site safety. In October, authorities companies and different organizations took web sites offline as a precaution over vital PHP vulnerabilities that might permit attackers to take management of servers. Polymarket additionally quickly suspended buying and selling on Oct. 29 after a third-party supplier was compromised, amid experiences of customers’ accounts being drained.
Journal: Banks are banning AI brokers over safety… and competitors considerations

