
The Ethereum Basis’s Trillion Greenback Safety initiative has recognized blind signing and transaction uncertainty as a person expertise danger, and is exploring native transaction assertions as a subsequent step to implement a transaction’s ultimate consequence, alongside Clear Signing.
This publish covers why a sound signature does not at all times assure the transaction end result you wished, how native transaction assertions might defend customers the place right this moment’s defenses cease, and the design selections behind them, with EIP-7906 (Transaction Assertions through State Diff Opcode) as one attainable strategy.
Two methods a signed transaction can go mistaken
The issue begins with how Ethereum works. It executes precisely what you authorize, with out judging whether or not the result’s what you wished. A signature commits to a request, however its consequence will depend on the code and state it encounters throughout execution. Customers have misplaced massive sums both as a result of they authorised one thing completely different from what they believed they had been approving, or as a result of the request they supposed nonetheless produced a end result they didn’t need.
The primary case is an intent mismatch, as seen within the Bybit incident and the BadgerDAO assault. In each assaults, a compromised frontend provided a signing request that differed from what customers believed they had been approving. Bybit’s signers approved changing the Protected’s implementation contract, whereas Badger customers granted the attacker permission to spend their tokens.
The opposite case is an consequence mismatch. The signer approves the request they had been proven, however its limits or the state it runs towards nonetheless permit a end result that conflicts with their financial objective or a standing security coverage. Within the Aave and CoW collateral swap, a person requested to swap about $50.4 million of aEthUSDT for aEthAAVE. AAVE liquidity was far too skinny for a commerce of that dimension. CoW’s gasoline ceiling additionally rejected the extra complicated quotes throughout verification, leaving one verified quote of roughly 329 aEthAAVE. The interface displayed a 99.9 p.c worth impression warning and required the person to substantiate that the whole worth might be misplaced. The person signed anyway and obtained tokens value about $36,000.
All three circumstances lacked a trusted rule over the ensuing state, outlined independently of the transaction builder and enforced throughout execution. Bybit’s rule would have required the authorised Protected implementation to stay unchanged. A Badger person’s rule would have allowed new token approvals just for printed Badger contracts. The Aave person’s rule would have set a minimal acceptable output, calculated independently of the quote proven by Aave’s interface (on this solver-based circulate, the signed order or CoW settlement protocol would even have needed to require the assertion).
Ethereum has no common mechanism for onchain code to examine the total set of web state adjustments and occasions produced by a transaction.
What a signature doesn’t management
Your signature commits to the motion you request, together with the goal, worth and calldata. The EVM executes your name towards the contract code and state current when the transaction runs, which can have modified because you signed. The ensuing web steadiness and storage adjustments, together with any emitted occasions, can due to this fact differ from what you anticipated.
The diagram under reveals how the signed request, code and state decide the end result.
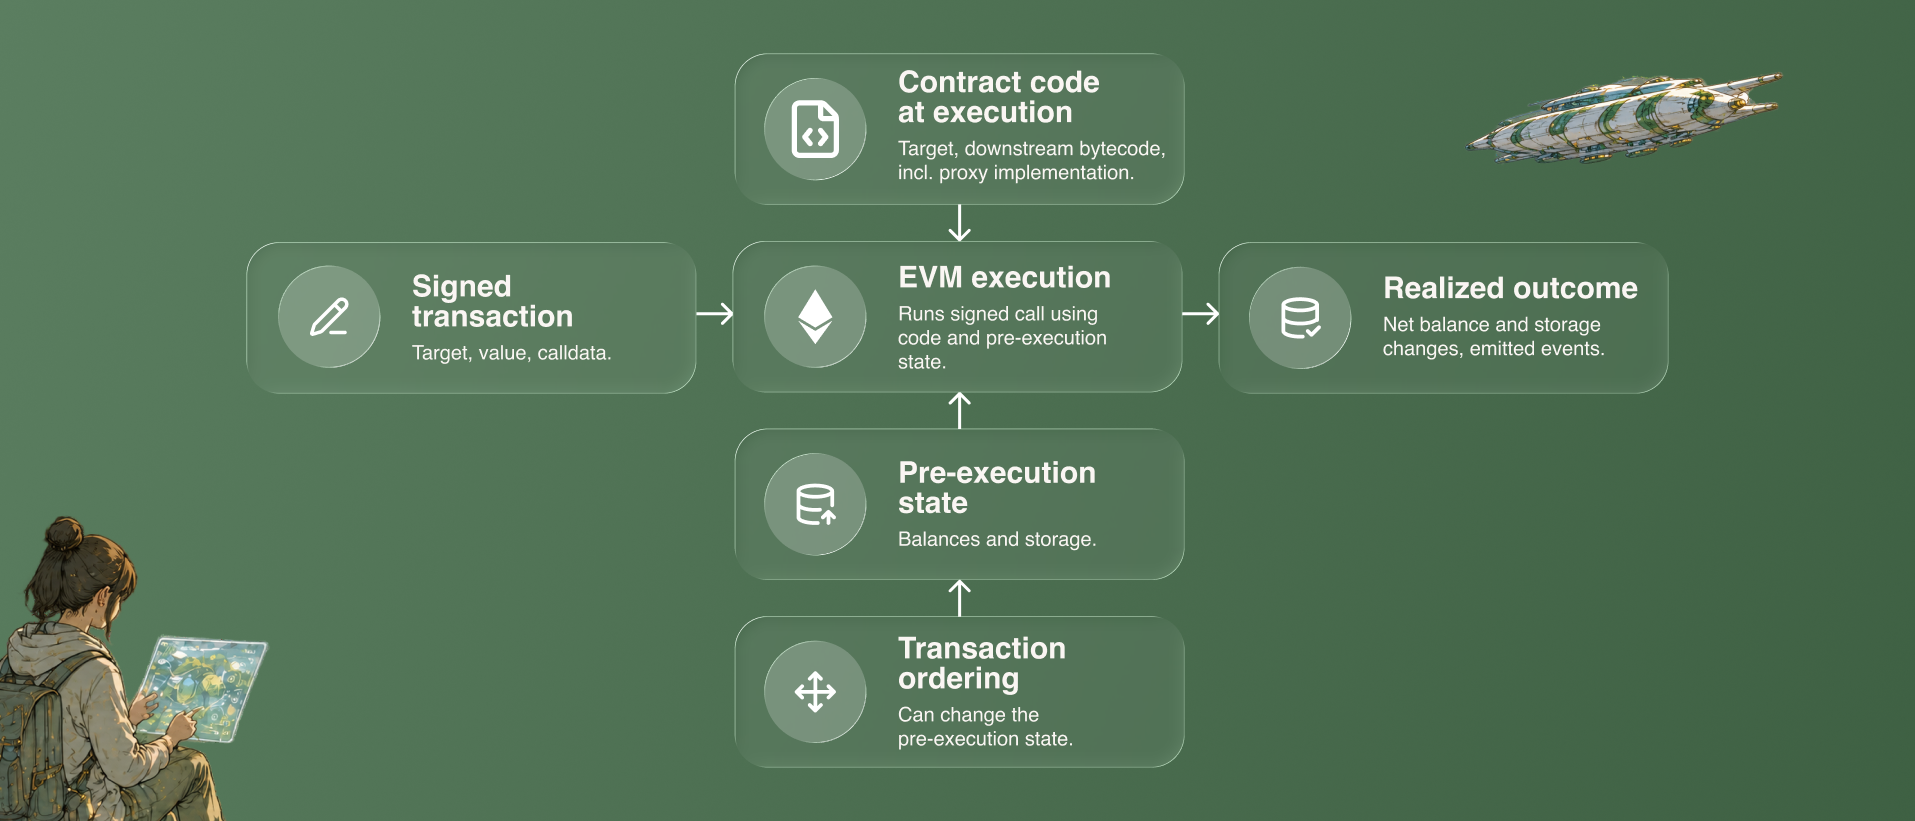
The goal contract, or one other contract it calls, could use a proxy whose implementation adjustments earlier than execution, so the code that runs can differ from what you inspected. Transaction ordering also can change the state your name encounters. For instance, a sandwich assault can shift a pool’s worth earlier than your swap executes with out altering your signed transaction.
The place right this moment’s defenses cease
A number of defenses are already in place. One is Clear Signing, which explains to the person what motion the calldata requests. It will depend on correct decoding and on the signer recognizing when that motion differs from what they supposed.
One other protection is simulation, which predicts a transaction’s results utilizing a specific chain state. The chain state can change earlier than inclusion, and the transaction signed could differ from the one simulated. In Radiant Capital’s case, each the pockets interface and the simulation confirmed the supposed transaction, whereas malware on the signers’ machines substituted a malicious payload at signing time.
Contract checks and pockets guards additionally implement guidelines throughout EVM execution. Uniswap, for instance, reverts a swap if its output falls under amountOutMinimum. Protected’s checkAfterExecution hook lets a guard examine the account’s state after execution and revert a transaction that violates its guidelines for house owners or configuration. Each approaches require selecting which state to verify upfront. To learn one other contract’s storage, they rely on the features it exposes. A token’s balanceOf makes steadiness checks simple, however a proxy needn’t expose its implementation deal with via a perform. With out such an interface, a guard can not learn the implementation slot instantly.
These checks can not examine the transaction’s full set of web state adjustments. A guard can confirm {that a} specific steadiness is unchanged, however it can not ask the EVM what else modified, so results it was not designed to verify can go unnoticed.
How native transaction assertions work
Native transaction assertions would let onchain code examine the total set of web state adjustments after the transaction’s actions have run. An assertion makes use of read-only logic to match beginning and ultimate values towards a rule. If the rule fails, the actions revert.
The rule is included within the transaction and signed together with its actions. It could cowl web adjustments to balances, storage and code, in addition to newly deployed contracts and emitted occasions. It could require a minimal quantity obtained, cap spending, block new approvals, protect an account’s management logic or permit solely a specified set of adjustments. The diagram under reveals how assertions verify the end result and revert the transaction’s actions if the foundations fail.
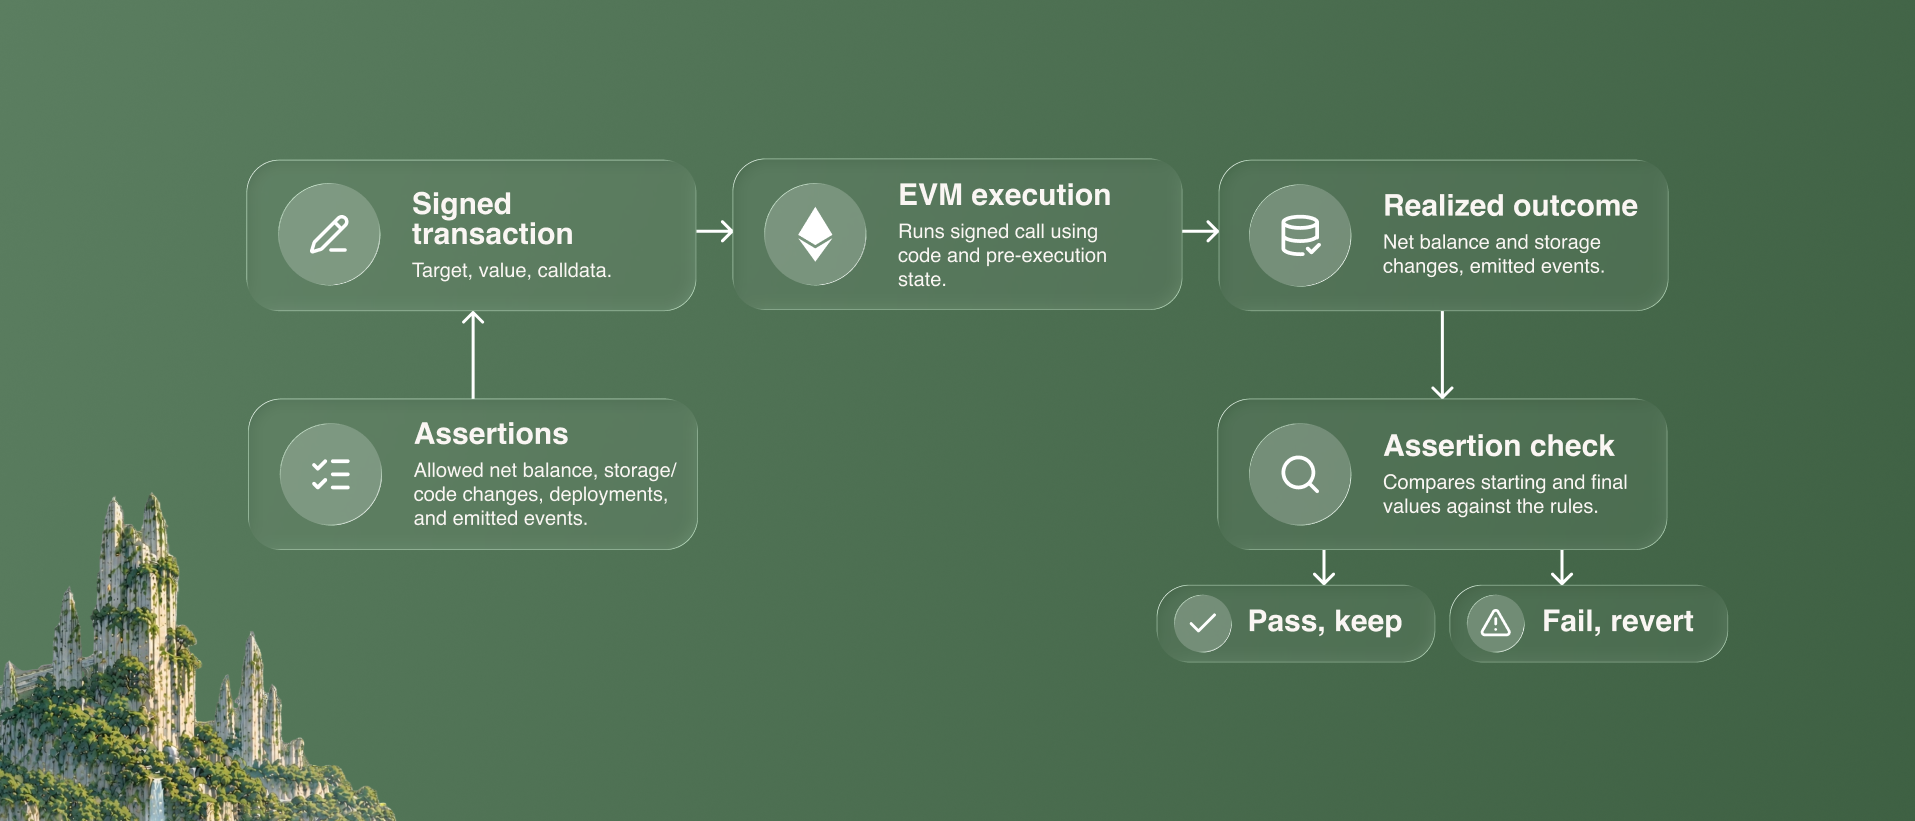
The rule’s supply issues as a lot because the verify itself. A compromised frontend can write an assertion that allows the assault. A helpful rule should come from independently authorised person intent, a standing account coverage or protocol logic that the compromised element can not change.
Three design selections
Designing native transaction assertions requires selections about what data the EVM exposes, how assertion code accesses it and the place the opcodes can run. The knowledge might embrace state adjustments, occasions or each. Entry choices embrace enumerating entries, trying up particular values or copying the total set of adjustments into reminiscence. The opcodes might be restricted to specific transaction varieties or execution phases, or allowed anyplace within the EVM.
EIP-7906 as a attainable resolution
One attainable strategy is EIP-7906, which builds on the body transactions outlined in EIP-8141. A body transaction accommodates an ordered sequence of validation and motion steps. EIP-7906 provides a read-only POST_TX body on the finish to verify the transaction’s consequence. EIP-8141 is scheduled for Hegotá, whereas EIP-7906 has superior to “Thought-about for Inclusion” however is just not but confirmed for the improve.
The design exposes each state adjustments and occasions. State adjustments are reported as web variations in native ETH balances and storage, alongside newly deployed contracts and their code hashes. A storage slot written 5 instances seems as one entry with its beginning and ultimate values. If the slot ends with its authentic worth, it doesn’t seem in any respect.
Three new opcodes (EVM directions) present entry to this data. TXTRACE enumerates web state adjustments and occasions, TXDIFF retrieves beginning and ultimate values for particular addresses and storage slots, and EVENTDATACOPY copies an occasion’s information into reminiscence.
These opcodes work solely inside a POST_TX body, which runs on the finish of the transaction as a static name. This lets the assertion examine the end result with out altering state. If the rule is violated, the whole execution physique reverts, however the transaction stays within the block with a failed standing and the gasoline payer is charged for the gasoline consumed. That cost prevents attackers from making builders execute intentionally failing transactions without cost.
The assertion must be required
EIP-7906 doesn’t require transactions to incorporate an assertion, so whoever builds the transaction can go away it out.
For the person’s personal transactions, the pockets should make sure that each body transaction it builds contains the required assertion. The rule can come from a simulation the pockets has run or from a standing coverage that applies to all its transactions.
A protocol’s protected perform should confirm that the decision comes from a body transaction containing the precise required assertion. It should reject unusual transactions and body transactions with a lacking or incorrect assertion. Callers and integrations would due to this fact want to make use of suitable body transactions, and an already deployed immutable contract couldn’t add this verify.
The place transaction assertions might assist
Past the safety advantages for customers and protocols, native transaction assertions might assist different use circumstances. They may, for instance, strengthen delegation. Whenever you let an agent act in your behalf, you’ll be able to restrict which contracts it makes use of, how a lot it spends and the way lengthy its permissions final. Assertions might add guidelines for the end result of every transaction, so you’ll be able to constrain each what the agent could do and what its actions produce.
A protocol might additionally outline its personal rule, requiring the identical security verify for each caller utilizing a body transaction. In solver execution, the protocol might specify the required consequence whereas leaving the solver free to decide on the route. That assure would apply solely inside one transaction on one community, so it could not cowl a route spanning a number of chains. Assertions might additionally verify {that a} workflow reaches its supposed ultimate state, with unused tokens returned to the person and any remaining token approvals revoked.
Assist form the design
Options for native transaction assertions are nonetheless being designed as a part of the Ethereum Basis’s Trillion Greenback Safety initiative, and we need to hear from the pockets and protocol groups who would use them. Get in contact at trilliondollarsecurity@ethereum.org to discover the use circumstances with us and assist form the analysis, or be a part of the EIP-7906 dialogue thread.
Learn extra about danger controls and precedence work at trilliondollarsecurity.org.

