
BTCPay Server has pushed an emergency replace to repair 5 newly disclosed flaws in nginx, the net server that sits in entrance of most BTCPay installations. The challenge is urging retailers who run their very own Bitcoin fee servers to replace as quickly as potential.
The repair doesn’t change the BTCPay Server model quantity. As an alternative, it updates the bundled nginx part to model 1.31.9, which nginx launched on Nov. 18 with fixes for 10 safety points.
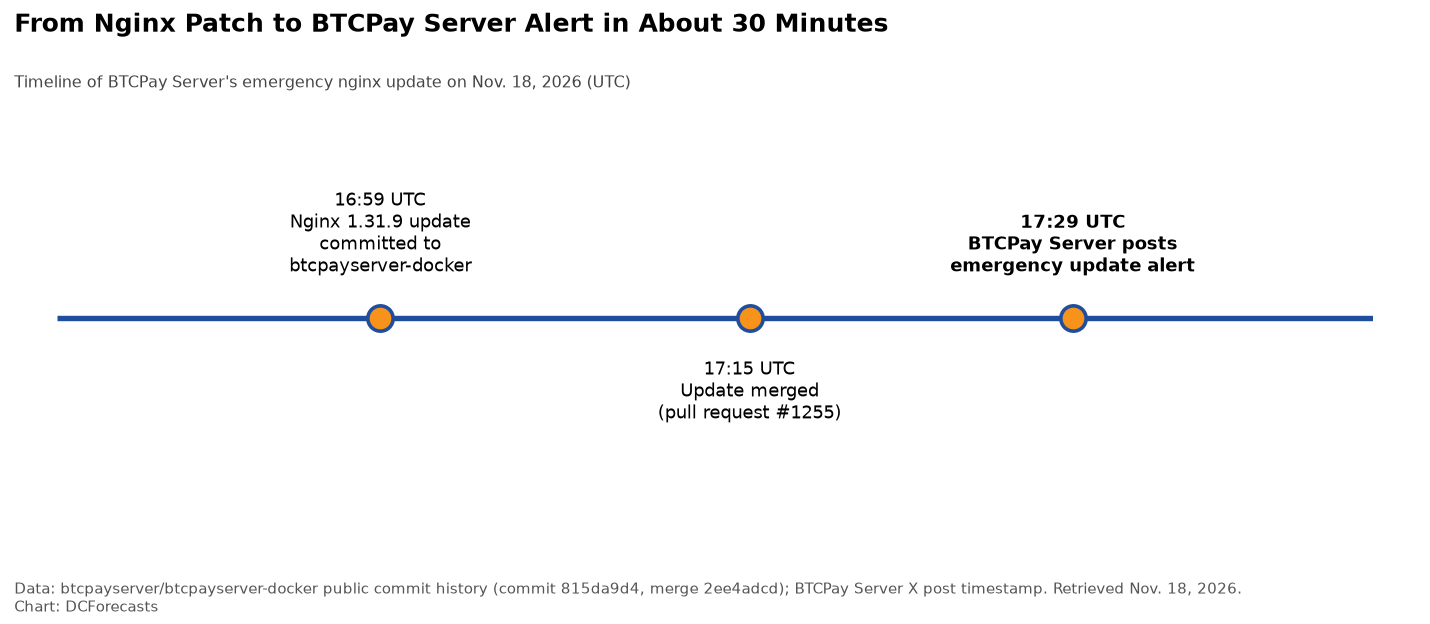
The velocity of the response stood out. Public commit data present the nginx improve landed in BTCPay’s Docker deployment repository at 16:59 UTC, was merged at 17:15 UTC, and the challenge’s alert went out at about 17:29 UTC.
5 Nginx Flaws Behind the Alert
In its announcement, BTCPay Server listed 5 CVEs: CVE-2026-123007, CVE-2026-123634, CVE-2026-123633, CVE-2026-121810 and CVE-2026-113425. All 5 are mounted in nginx 1.31.9 on the mainline department and 1.30.7 on the secure department, based on nginx’s safety advisories.
Essentially the most critical is CVE-2026-123007, rated main by nginx. It’s a reminiscence corruption bug in HTTP/2 circulate management. Nginx’s change log says a circulate management window overflow would possibly let an attacker crash a employee course of, “or may need potential different affect.”
Two of the opposite flaws are use-after-free bugs in HTTP/2 and HTTP/3. One other impacts the resolver, and the fifth, additionally rated main, is within the mail proxy module.
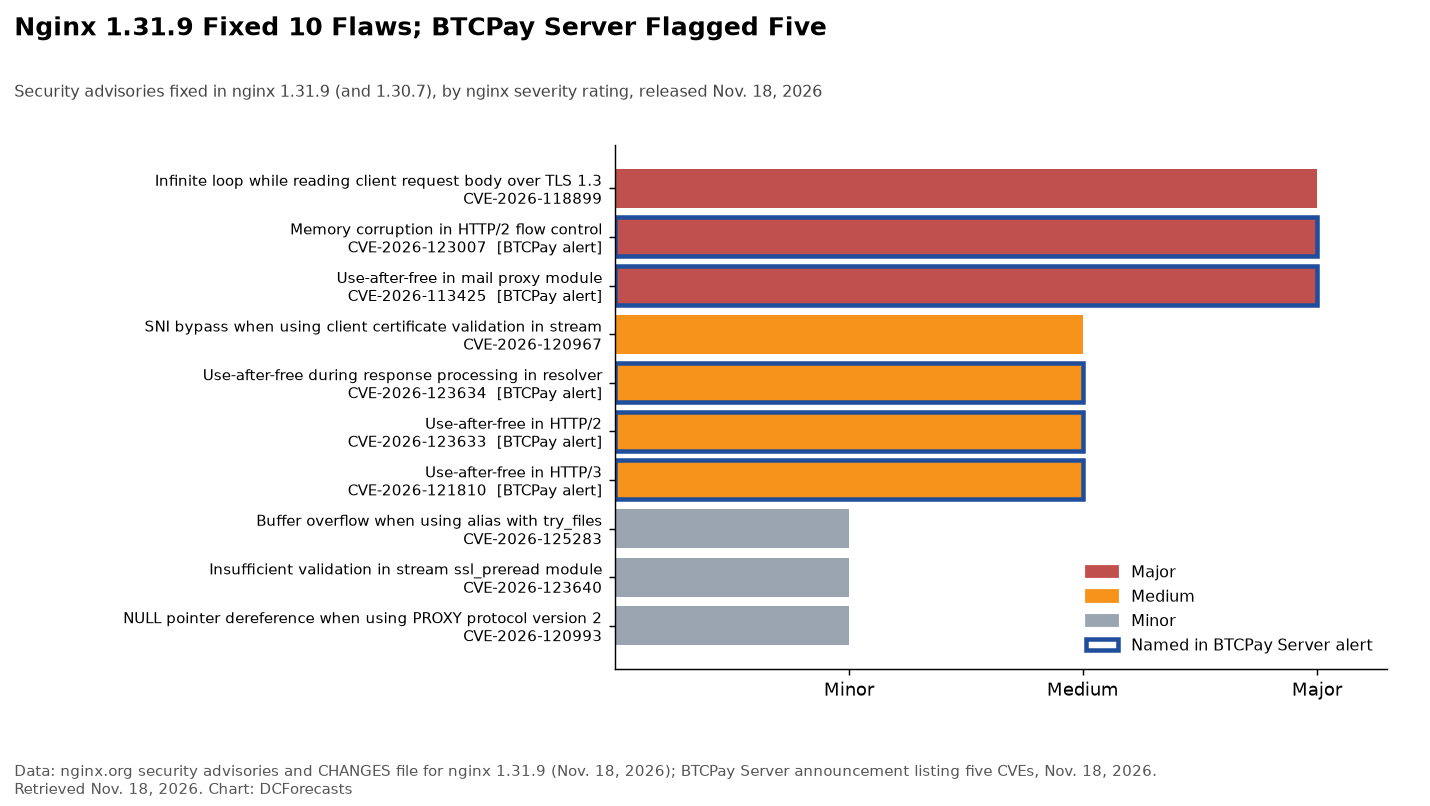
The nginx launch additionally fixes 5 extra points that BTCPay didn’t identify, together with an infinite loop when studying request our bodies over TLS 1.3, which nginx charges main.
Why Nginx Issues to a Bitcoin Fee Server
In the usual BTCPay Server Docker deployment, nginx works because the entrance door. It accepts incoming connections on the same old internet and HTTPS ports and routes every request to the fee software or to different providers operating on the identical machine.
That makes it the primary piece of software program an out of doors customer touches, whether or not it’s a buyer paying an bill or somebody probing the server. A flaw there can expose the entire field, even when the fee software program behind it’s sound.

ADVERTISEMENT
It additionally explains why the repair got here as a dependency replace quite than a brand new BTCPay launch. The fee code didn’t change. Solely the part in entrance of it did, which allowed the crew to ship rapidly with out ready for a full launch cycle.
The identical strategy applies to different providers within the deployment. Up to now week alone, the repository’s public historical past reveals routine updates to bundled parts reminiscent of Tor and the Mempool block explorer.
How Retailers Can Replace
For many operators, the repair is an ordinary server replace. Directors can run it from the BTCPay Server dashboard below the server settings and upkeep part, or from the command line with the challenge’s replace script on Docker installations.
As a result of the BTCPay model quantity stays the identical, the challenge advised customers how you can test that the repair is in place. Operating a model test contained in the nginx container ought to now report nginx 1.31.9. A BTCPay account replying to customers described the change as “a dependency replace,” including that the following model of BTCPay is in testing.
Customers who run BTCPay via node platforms reminiscent of Umbrel or Start9 want to attend for these platforms to ship the replace. For anybody who can not replace instantly, a core contributor shared a short lived workaround that turns off HTTP/2 in nginx.
No Confirmed Assaults So Far
BTCPay Server was cautious to not overstate the hazard. In a put up on Nov. 18, the challenge mentioned it understands that “the referenced Nginx exploits are fragile and that, thus far, no assaults have been publicly confirmed.”
“However as a FOSS challenge, we’ll at all times act as quickly as potential to supply remediations for customers,” it added.
That issues as a result of BTCPay is self-hosted. There is no such thing as a central firm holding buyer funds or pushing silent fixes to each server. Every service provider runs and updates their very own node, so a transparent, quick warning is the principle line of protection.
Open-Supply Safety at Work
That is how open-source Bitcoin infrastructure is meant to work. A broadly used internet server ships a safety launch, and inside hours a volunteer-driven fee challenge has examined it, merged it and advised its customers precisely what to do.
BTCPay Server thanked its sponsors in the identical thread, noting that their assist retains its open-source work sustainable so it “can sustain with safety updates.” Among the many backers it named have been OpenSats, Spiral, Tether and the Human Rights Basis. OpenSats individually funded 21 Bitcoin initiatives in its newest grant wave this week.
In our view, that assist is cash nicely spent. BTCPay lets retailers settle for Bitcoin immediately, with no intermediary and no charges to a fee processor, and a quick safety response is a part of what makes self-custody sensible for companies.
The incident can also be a reminder that almost all crypto safety issues sit across the edges, in servers, assist instruments and dependencies, quite than in Bitcoin itself. Earlier at the moment, Etherscan and LOBSTR reported assaults on their buyer assist techniques, which run on third-party assist desk software program. No funds have been misplaced in both case.
What Operators Ought to Do Now
Retailers operating BTCPay Server ought to set up the replace, affirm that nginx experiences model 1.31.9, and control their node platform in the event that they use Umbrel or Start9.
Those that should delay ought to apply the HTTP/2 workaround as a stopgap solely. The nginx launch fixes issues past HTTP/2, so the total replace stays the actual repair.
DC Forecasts is a pacesetter in lots of crypto information classes, striving for the best journalistic requirements and abiding by a strict set of editorial insurance policies. In case you are to supply your experience or contribute to our information web site, be happy to contact us at [email protected]

