

Banks might ask fintech suppliers how they plan to guard buyer information and funds from future quantum threats earlier than regulators set expectations for these suppliers immediately.
The Singapore Fintech Affiliation (SFA) flagged that chance in a brand new report that units out what fintechs can do within the first 12 months of getting ready for quantum-safe migration.
No publicly identified quantum laptop can break the public-key cryptography that monetary companies depend on in the present day.
Changing it could actually take years as a result of it’s constructed into every part from fee techniques to cloud companies.

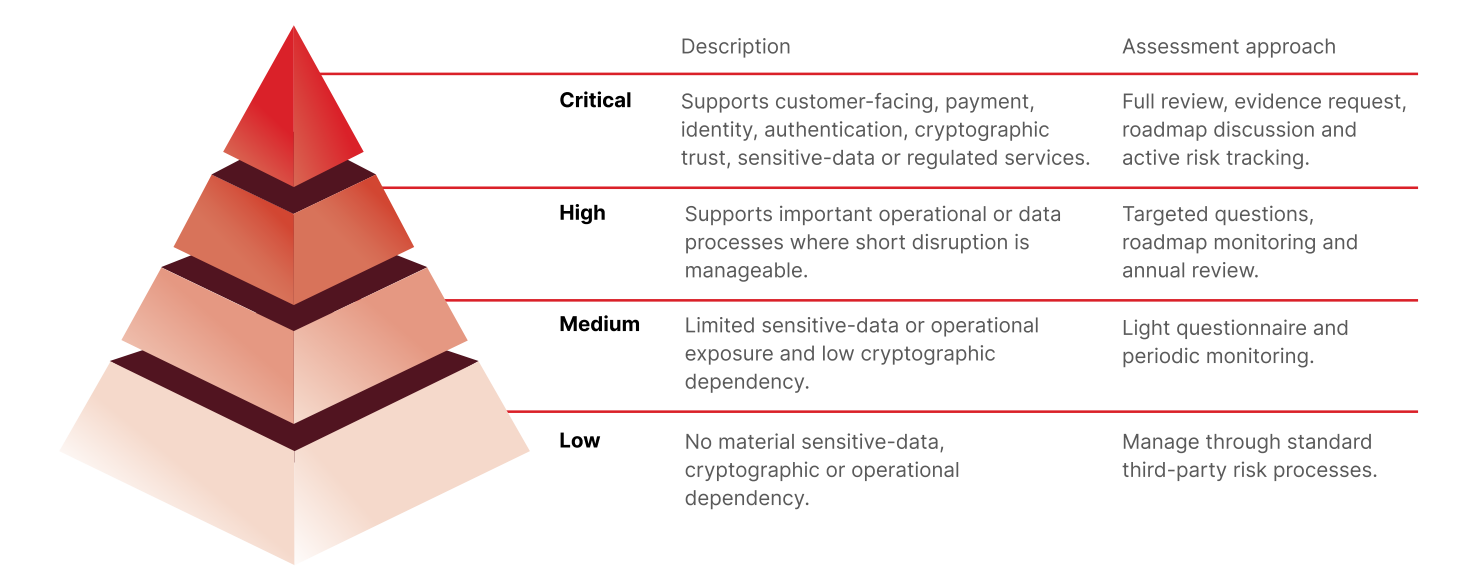
The report recommends prioritising information that want to remain personal for years, resembling buyer identification particulars and monetary histories.
Attackers might accumulate encrypted information now and decrypt them later if quantum computer systems change into highly effective sufficient.
These advances might additionally let attackers forge digital signatures used to confirm who authorised a fee or whether or not a software program replace is real.
What Fintechs Can Do Earlier than They Improve
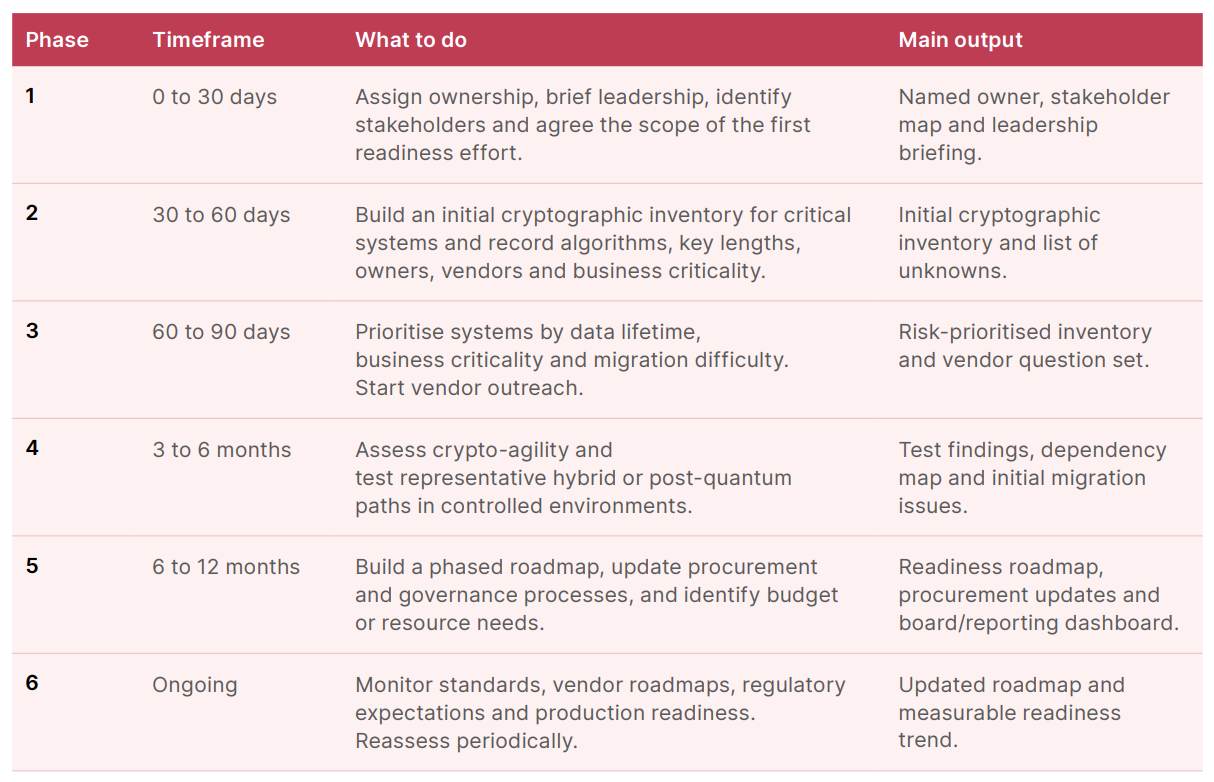
The SFA recommends placing somebody in cost and briefing senior administration within the first month.
Corporations can then test which cryptographic strategies their most necessary techniques use and ask cloud suppliers and fee processors once they plan to improve.
That may assist companies work out which adjustments their suppliers will make and which of them they should deal with themselves.
The report recommends testing upgrades in a managed atmosphere.
Some post-quantum strategies use bigger digital keys and signatures, which might have an effect on how rapidly techniques reply and whether or not they nonetheless work with techniques run by companions.
MAS Proposes a 2034 Goal for Monetary Corporations to Go Quantum-Protected
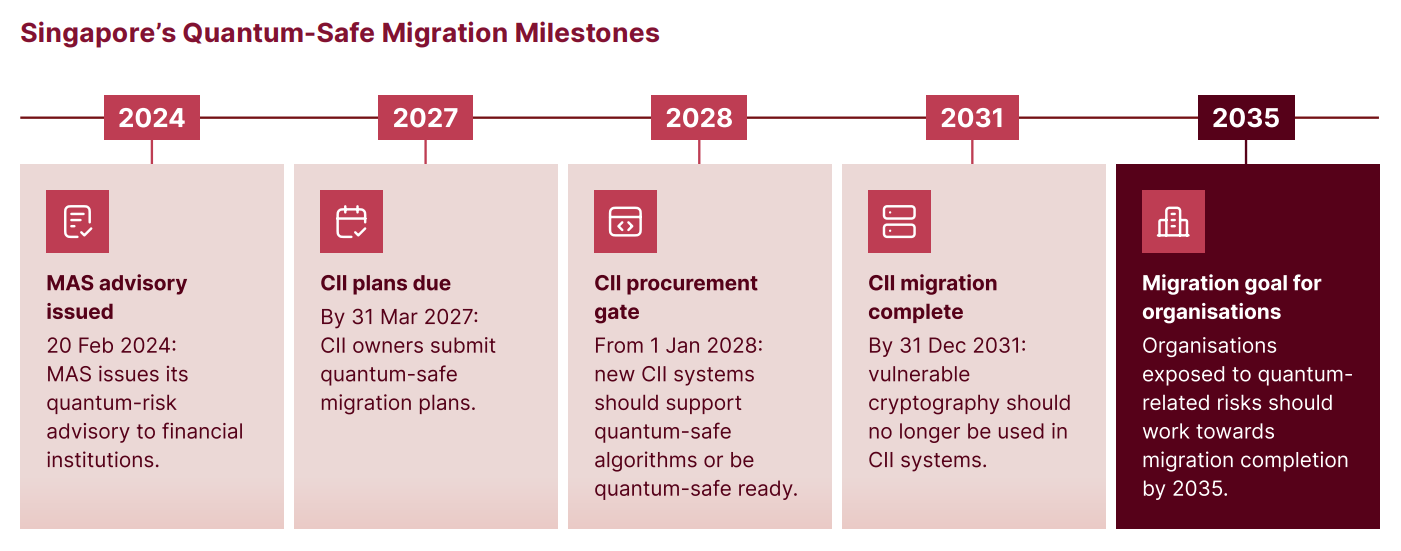
The Financial Authority of Singapore (MAS) is consulting on a proposal for many monetary establishments to have a migration plan by the top of 2027 and full the change for essential techniques by the top of 2030.
The proposed goal for all remaining techniques is the top of 2034.
The Cyber Safety Company of Singapore has inspired different organisations uncovered to quantum dangers to organize a plan by the top of 2027 and intention to finish migration by 2035.
Pramodh Rai, Chairman of the SFA Cyber Safety & Quantum Computing Subcommittee and Co-founder and CEO of Cyber Sierra, stated,
“Each fintech in Singapore depends on cryptography it didn’t write and, normally, can’t see, from the fee APIs it connects to, to the certificates behind its cloud companies. For many of them the primary requirement will are available in a financial institution’s vendor questionnaire, nicely earlier than any regulation.
Begin with the fundamentals: know which algorithms you rely upon, who owns them, how lengthy the information they shield should keep secret, and what your suppliers plan to do about it. This report provides companies a sensible place to start out.”
Featured picture: Edited by Fintech Information Singapore, primarily based on picture by dit26978 through Magnific

