

Trezor says a hacker took the names, cellphone numbers and residential addresses linked to about 27,000 of its {hardware} pockets orders. The breach didn’t occur at Trezor itself. It hit Skladon, one of many supply companions that ships Trezor gadgets to consumers in lots of nations.
The essential level for house owners: no cash, pockets backups, PINs or passphrases have been uncovered. Trezor says its personal programs weren’t compromised and that gadgets stay safe. What leaked is delivery information, and that’s nonetheless an actual threat for the individuals on the listing.
What Trezor disclosed on Monday
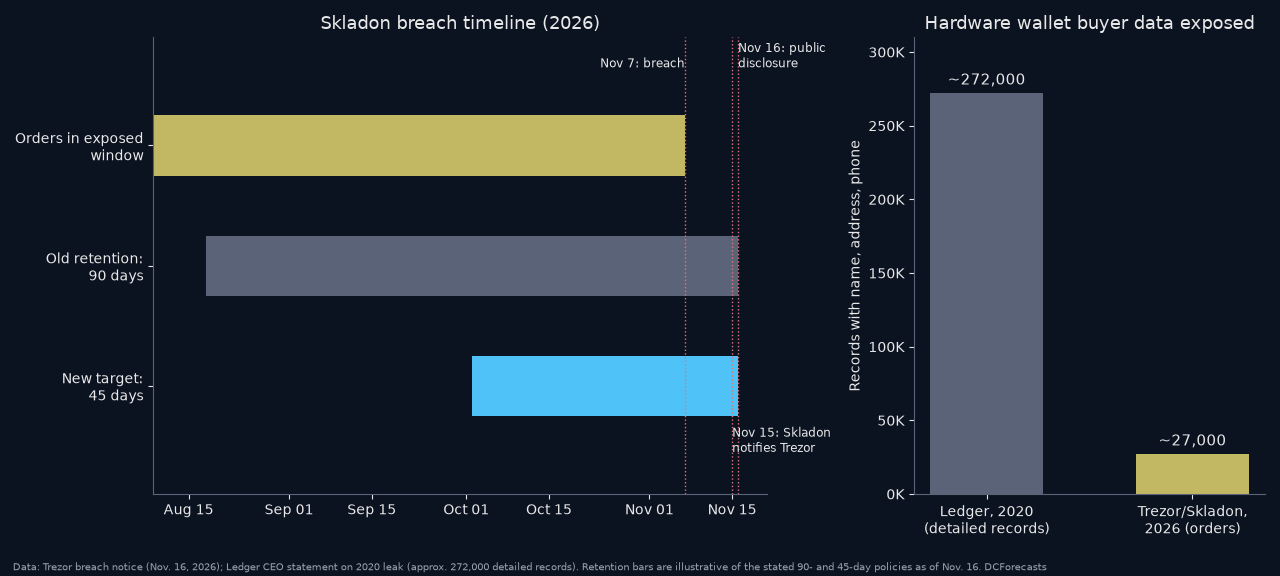
In a discover printed on November 16, Trezor stated Skladon advised it on November 15 that an attacker had gained unauthorized entry to its programs. In keeping with Trezor, the breach itself passed off on November 7.
“We imagine the attacker exported information for about 27,000 orders positioned between 9 August and seven November 2026,” the corporate wrote. It added that the investigation is ongoing.
The uncovered fields have been:
- Full names
- Cellphone numbers
- Supply addresses
- E-mail addresses
- Order dates, product names and costs
Trezor has emailed clients whose orders fall inside that window. A small group who ordered between August 9 and 14 can also be affected, however Trezor can not attain them by e mail. Their particulars had already been anonymized in its personal programs below its 90-day retention rule, whereas the copy held by the delivery associate survived.
Skladon doesn’t ship to the USA, so U.S. consumers are usually not affected, the corporate stated.
Why a Trezor information breach is a phishing downside, not a pockets downside
A {hardware} pockets retains non-public keys offline. Nothing in an order report can transfer bitcoin from a correctly secured gadget. That’s the reason this Trezor information breach doesn’t break the gadget’s core promise.
The hazard is social. Scammers who know a purchaser’s title, deal with and precise buy can sound very convincing. Trezor warned that criminals could quote actual order particulars in calls, texts, emails and even paper letters. It additionally advised clients to “be alert to potential dangers to your bodily safety.”

ADVERTISEMENT
Trezor phishing campaigns normally finish with one request: kind your restoration phrase into an internet site or a type. The corporate was blunt about this. Trezor won’t ever cold-call clients and can by no means ask for a pockets backup. Anybody who asks for these 12, 20 or 24 phrases is a thief.
Good {hardware} pockets safety habits cowl the remaining. Purchase solely from the maker or approved resellers, test firmware updates by the official app, and deal with any “pressing” message about your order as suspect. House owners holding bigger sums can add a passphrase, which creates a hidden pockets {that a} stolen backup alone can not open.
Smaller than Ledger’s 2020 leak, however a well-known sample
This isn’t the primary time pockets consumers’ delivery particulars have escaped. In 2020, rival maker Ledger first confirmed that about 1 million e mail addresses and 9,532 detailed buyer information had been stolen from its e-commerce database. Months later, a public dump confirmed the true determine for detailed information, with names, postal addresses and cellphone numbers, was roughly 272,000, based on an announcement from Ledger’s CEO.
At about 27,000 orders, the Skladon breach is roughly a tenth of that measurement. Trezor didn’t cover the sample, although. “We all know this isn’t the primary time buyer contact particulars and addresses have been uncovered in an incident involving certainly one of our companions,” it wrote, apologizing to clients hit greater than as soon as.
The weak level retains exhibiting up on the edges. It’s in e-commerce databases, assist desks and delivery companies, not within the gadgets or in Bitcoin itself. Final week we lined a unique supply-chain scare, when a hidden board discovered inside three Trezor Protected 5 wallets led Trezor to chop resellers.
Nameless pickup and shorter retention
Trezor’s repair goes after the basis trigger: holding much less information. From Monday, nameless pickup is stay in 18 European nations. Patrons want solely a sound e mail deal with and may gather a pockets from a parcel locker or pickup level. No actual title, residence deal with or cellphone quantity is required.
The corporate can also be reducing how lengthy it retains order information from 90 days to 45, with plans to go decrease. It is going to require its delivery companions to observe the identical coverage, and it says it’s reviewing its third-party relationships and the safety guidelines it units for them.
That strategy matches Bitcoin’s founding thought. The most secure private information is information that was by no means collected. A purchaser who orders a pockets anonymously and picks it up from a locker leaves far much less behind for the subsequent leak to reveal.
What affected consumers ought to do now
- Verify your inbox for Trezor’s discover in case you ordered between August 9 and November 7.
- By no means enter or share your restoration phrase, regardless of the message claims.
- Attain Trezor Assist solely by typing the official web site deal with your self.
- Watch out about who learns that you just maintain bitcoin, and maintain your property deal with non-public the place you’ll be able to.
Cash on a Trezor are as protected as we speak as they have been final week, so long as the backup stays secret. A Trezor hack of the gadget itself has not occurred right here. What has occurred is that 27,000 consumers at the moment are extra prone to be focused by scammers.
Self-custody stays the strongest solution to maintain bitcoin. Monday’s breach is a reminder that sturdy self-custody additionally means sharing much less private information whenever you purchase the gadget.
DC Forecasts is a frontrunner in lots of crypto information classes, striving for the very best journalistic requirements and abiding by a strict set of editorial insurance policies. If you’re to supply your experience or contribute to our information web site, be happy to contact us at [email protected]

